Understanding threatsThreats FrameworksSVG
Two threats and the references they share
Choose two threats or one of the suggested pairs with a large overlap. The middle column shows the references both point to; the outer ones show what applies to only one of them. The mitigations of both sides are listed below.
For anyone drafting policies, training material or audit plans
Threat comparison
11shared references
5only in the first
1only in the second
4 to 6mitigations in the catalogue
2/5shared effect classes
Only Backdoor ML Model5
Model and Training Data Manipulation · Development
BIML BIML78 model:2 BSI R20 NIST AI RMF NISTAML.021 NIST AI RMF NISTAML.026 OWASP LLM Top 10 LLM04:2026
Shared by both11
the same reference in the same framework
BIML BIML-LLM model:4 BSI R19 EU AI Act Article 53(1)(a) EU AI Act Article 55(1)(a) EU AI Act Article 9(1), 9(2)(a), 9(2)(d) MITRE ATLAS AML.T0018 NIST AI RMF MEASURE 2.7 NIST AI RMF NISTAML.023 NIST AI RMF NISTAML.051 NIST AI RMF Section 2.9 OWASP LLM Top 10 LLM05:2026
Only Sleepy Agent (Time/Event-Triggered Hidden Instructions)1
Model and Training Data Manipulation · Development
Backdoor ML Model 4 mitigations
The model contains hidden behavior, a backdoor. It works correctly on normal inputs; only a secret trigger pattern in the input flips the output to whatever result the attacker has chosen.
-
Model scanning for backdoors
Reason for the classification
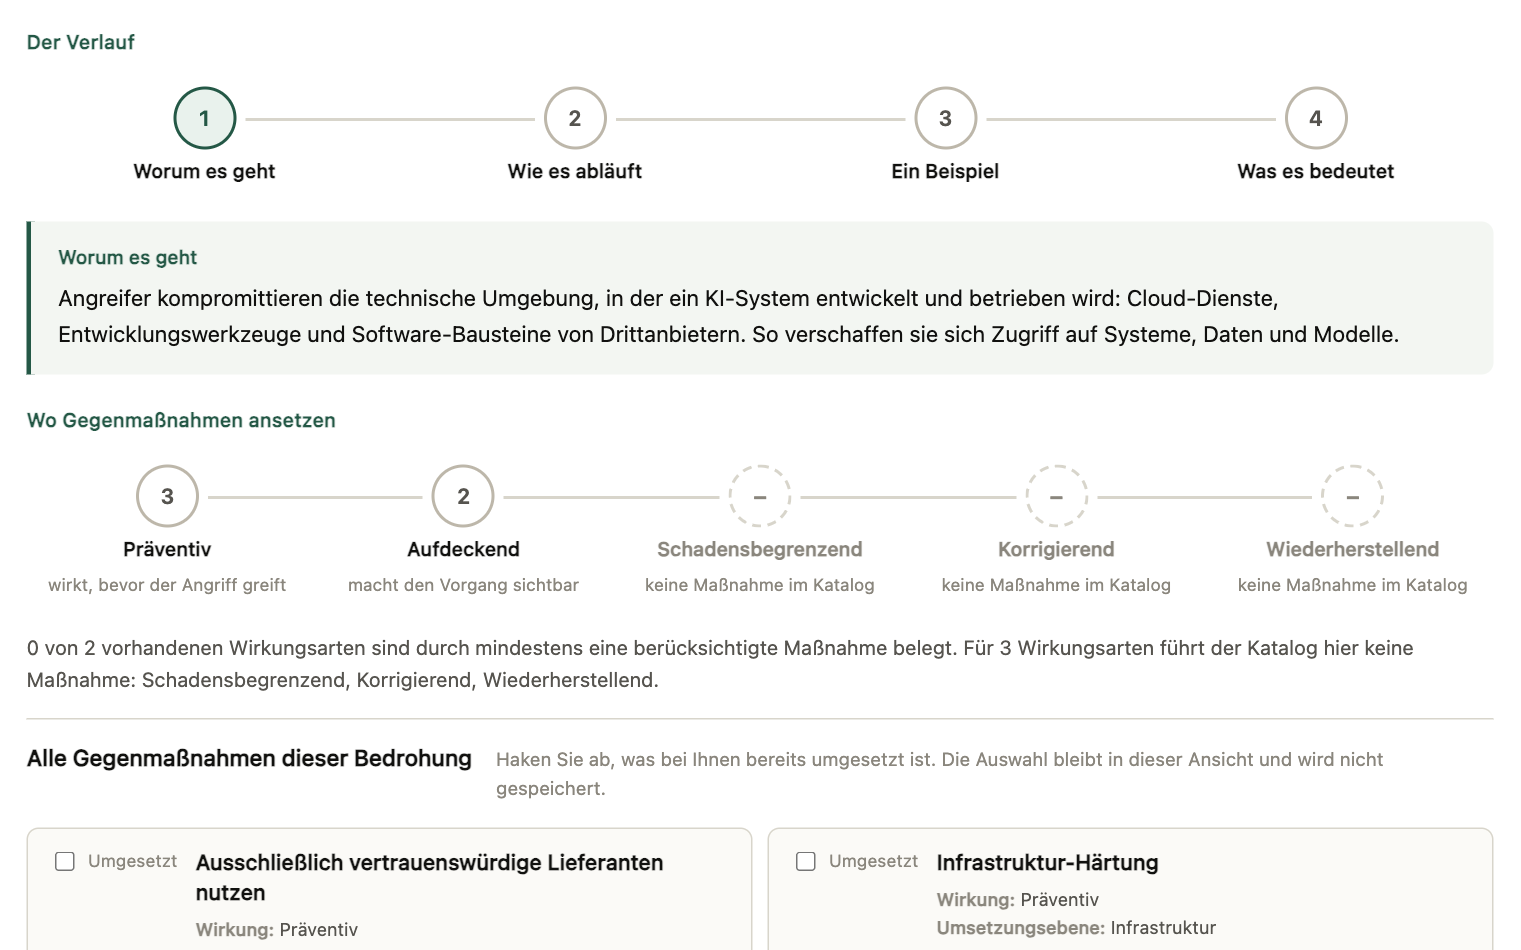
Primarily technical: Software or analytical tools systematically produce and evaluate measurements, deviations, or attack indicators.
-
Neural cleanse techniques
Reason for the classification
Primarily technical: Software or analytical tools systematically produce and evaluate measurements, deviations, or attack indicators.
-
Activation clustering analysis
Reason for the classification
Primarily technical: Software or analytical tools systematically produce and evaluate measurements, deviations, or attack indicators.
-
Train from trusted base models only
Reason for the classification
Primarily organizational and process-based: Defined selection, operating, or lifecycle procedures make the control binding and repeatable; complemented by technical implementation.
Sleepy Agent (Time/Event-Triggered Hidden Instructions) 6 mitigations
Malicious logic lies dormant inside the model and only activates later: on a set date, at a specific event, or in a particular environment. Until then, the system passes every test and review without raising suspicion.
-
Behavioral analysis under diverse conditions
Reason for the classification
Primarily technical: Software or analytical tools systematically produce and evaluate measurements, deviations, or attack indicators.
-
Time-shifted testing
Reason for the classification
Primarily technical: Software or analytical tools systematically produce and evaluate measurements, deviations, or attack indicators.
-
Adversarial evaluation across contexts
Reason for the classification
Primarily technical: Software or analytical tools systematically produce and evaluate measurements, deviations, or attack indicators.
-
Runtime behavior monitoring
Reason for the classification
Primarily technical: Software or analytical tools systematically produce and evaluate measurements, deviations, or attack indicators; complemented by binding workflows.
-
Model interpretability tools
Reason for the classification
Primarily technical: Software or analytical tools systematically produce and evaluate measurements, deviations, or attack indicators.
-
Supply chain integrity verification
Reason for the classification
Primarily technical: Software or analytical tools systematically produce and evaluate measurements, deviations, or attack indicators; complemented by binding workflows.
Threat pathwayThe threat pathway shows how one of these threats unfolds in detail.
The file shows the current state including any filters and carries the note, catalogue version and source.
A shared reference means that both threats point to the same place in the same framework. It does not mean that one mitigation covers both.
Versatile AI Risk Assessment is an aid for structuring AI risks and making them transparent. It does not replace legal or professional advice and makes no binding decisions.
Further analyses
The same data, a different question
The other nine analyses, searchable and filterable by perspective like the overview; those of the same perspective first.
Show filters
No filter set, the list shows the complete collection.9 of 9 further analyses
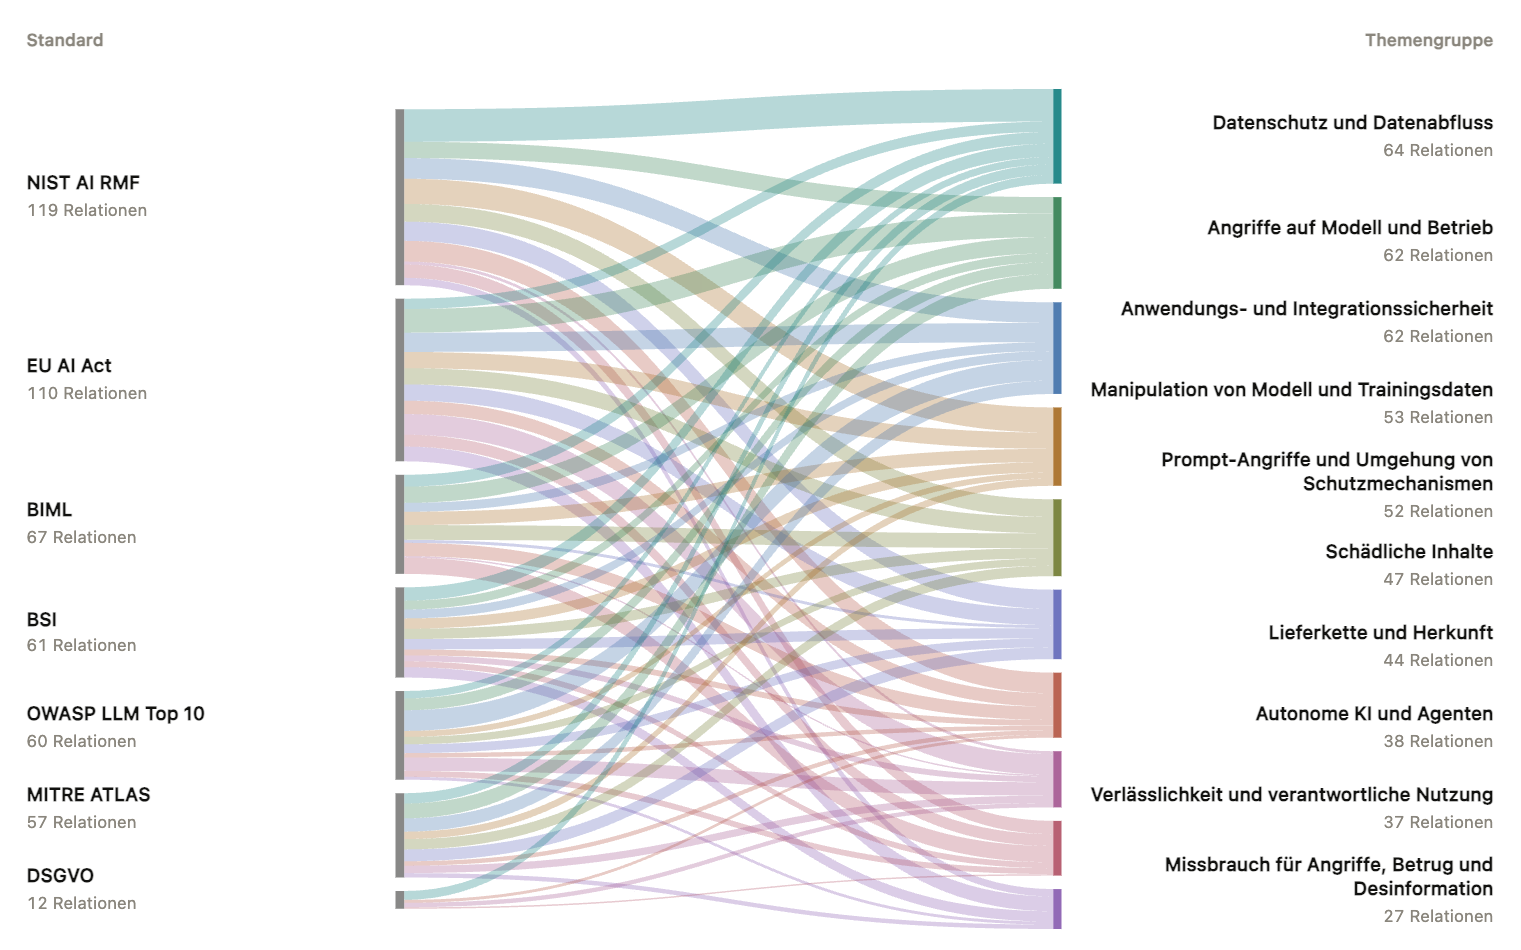
Checking frameworks and evidence
Framework mappings
Where is this anchored professionally and legally?
No result for this selection.
Remove a filter or clear the search. The numbers in the filter column show how many entries the collection holds for each value.
Related
From the analysis to the assessment
All 52 threats in full: description, impact, example, mitigations and verified sources.
To the catalogueSix questions along the EU AI Act and a deadline plan with the obligations that apply to your system.
To the quick checkChoose a role and a risk class and see which EU AI Act obligations apply from when, with legal reference and evidence.
To the obligations compassThe full assessment with system context, threat selection and evidence tracking, free of charge in the browser.
To the live demo