Versatile AI Risk Assessment

486 verified relations between seven frameworks and ten topic groups

Each ribbon connects a framework with a topic group of the catalogue; its thickness corresponds to the number of verified relations. Select a framework or a group to see the concrete references. For the EU AI Act and the GDPR, the applicability condition of the respective provision is shown as well.

Who it is for: For compliance, legal, internal audit and assurance

Framework mappings

Flow diagram of the verified relations 486 verified relations connect 7 frameworks with 10 topic groups. Ribbon thickness corresponds to the number of relations. All values are also given in the labels and in the list below. NIST AI RMF · Privacy and Data Leakage: 22NIST AI RMF · Attacks on the Running Model and Service: 11NIST AI RMF · Application and Integration Security: 14NIST AI RMF · Model and Training Data Manipulation: 17NIST AI RMF · Prompt Attacks and Guardrail Evasion: 12NIST AI RMF · Harmful Content: 13NIST AI RMF · Supply Chain and Provenance: 14NIST AI RMF · Agentic and Autonomous AI: 2NIST AI RMF · Reliability and Responsible Use: 9NIST AI RMF · Malicious Use for Attacks, Fraud and Disinformation: 5EU AI Act · Privacy and Data Leakage: 7EU AI Act · Attacks on the Running Model and Service: 16EU AI Act · Application and Integration Security: 13EU AI Act · Model and Training Data Manipulation: 11EU AI Act · Prompt Attacks and Guardrail Evasion: 11EU AI Act · Harmful Content: 11EU AI Act · Supply Chain and Provenance: 9EU AI Act · Agentic and Autonomous AI: 14EU AI Act · Reliability and Responsible Use: 8EU AI Act · Malicious Use for Attacks, Fraud and Disinformation: 10BIML · Privacy and Data Leakage: 8BIML · Attacks on the Running Model and Service: 11BIML · Application and Integration Security: 6BIML · Model and Training Data Manipulation: 9BIML · Prompt Attacks and Guardrail Evasion: 10BIML · Harmful Content: 2BIML · Supply Chain and Provenance: 9BIML · Agentic and Autonomous AI: 1BIML · Reliability and Responsible Use: 11BSI · Privacy and Data Leakage: 9BSI · Attacks on the Running Model and Service: 6BSI · Application and Integration Security: 6BSI · Model and Training Data Manipulation: 7BSI · Prompt Attacks and Guardrail Evasion: 7BSI · Harmful Content: 7BSI · Supply Chain and Provenance: 4BSI · Agentic and Autonomous AI: 4BSI · Reliability and Responsible Use: 4BSI · Malicious Use for Attacks, Fraud and Disinformation: 7OWASP LLM Top 10 · Privacy and Data Leakage: 5OWASP LLM Top 10 · Attacks on the Running Model and Service: 8OWASP LLM Top 10 · Application and Integration Security: 14OWASP LLM Top 10 · Model and Training Data Manipulation: 4OWASP LLM Top 10 · Prompt Attacks and Guardrail Evasion: 5OWASP LLM Top 10 · Harmful Content: 6OWASP LLM Top 10 · Supply Chain and Provenance: 3OWASP LLM Top 10 · Agentic and Autonomous AI: 9OWASP LLM Top 10 · Reliability and Responsible Use: 4OWASP LLM Top 10 · Malicious Use for Attacks, Fraud and Disinformation: 2MITRE ATLAS · Privacy and Data Leakage: 7MITRE ATLAS · Attacks on the Running Model and Service: 10MITRE ATLAS · Application and Integration Security: 9MITRE ATLAS · Model and Training Data Manipulation: 5MITRE ATLAS · Prompt Attacks and Guardrail Evasion: 7MITRE ATLAS · Harmful Content: 8MITRE ATLAS · Supply Chain and Provenance: 3MITRE ATLAS · Agentic and Autonomous AI: 5MITRE ATLAS · Malicious Use for Attacks, Fraud and Disinformation: 3GDPR · Privacy and Data Leakage: 6GDPR · Supply Chain and Provenance: 2GDPR · Agentic and Autonomous AI: 3GDPR · Reliability and Responsible Use: 1

486 verified relations from 21 primary sources. Select a framework on the left or a topic group on the right.

Nothing selected yet. Each ribbon connects a framework with a topic group.

The file shows the current state including any filters and carries the note, catalogue version and source.

Mappings indicate relevance and applicability, not evidence of compliance. The applicability condition states the preconditions under which a provision applies at all.

Versatile AI Risk Assessment is an aid for structuring AI risks and making them transparent. It does not replace legal or professional advice and makes no binding decisions.

Checking frameworks and evidence

The same data, a different question

Which provision applies, what it does not reach and which primary source the catalogue relies on.

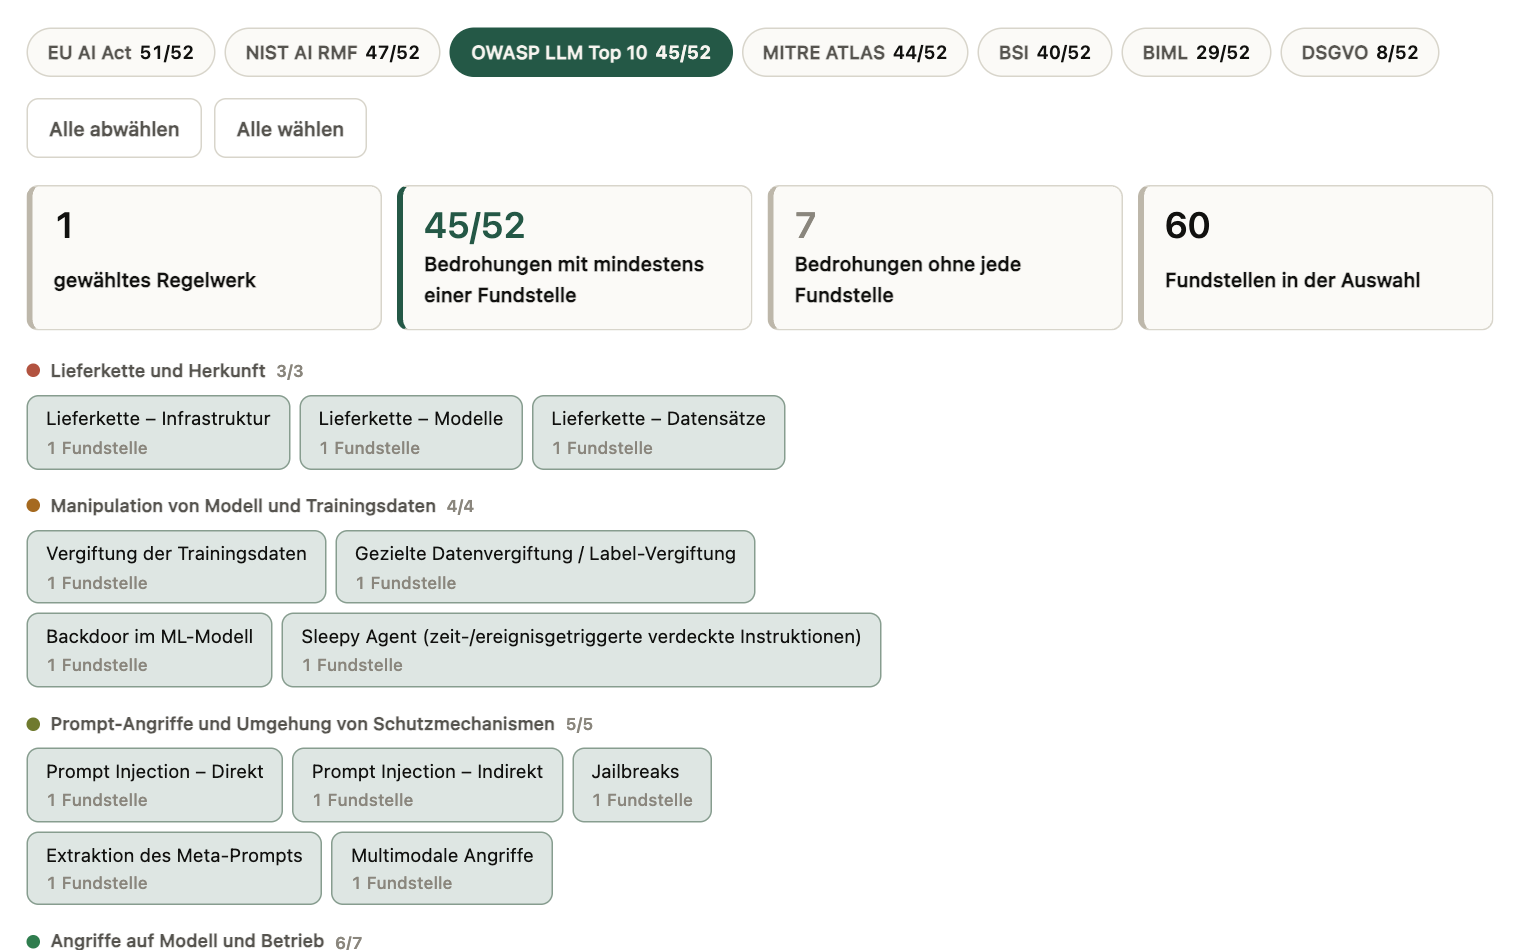
  1. Preview of the analysis: Coverage gaps Coverage gaps What does my framework not reach? For anyone choosing a framework or already committed to one
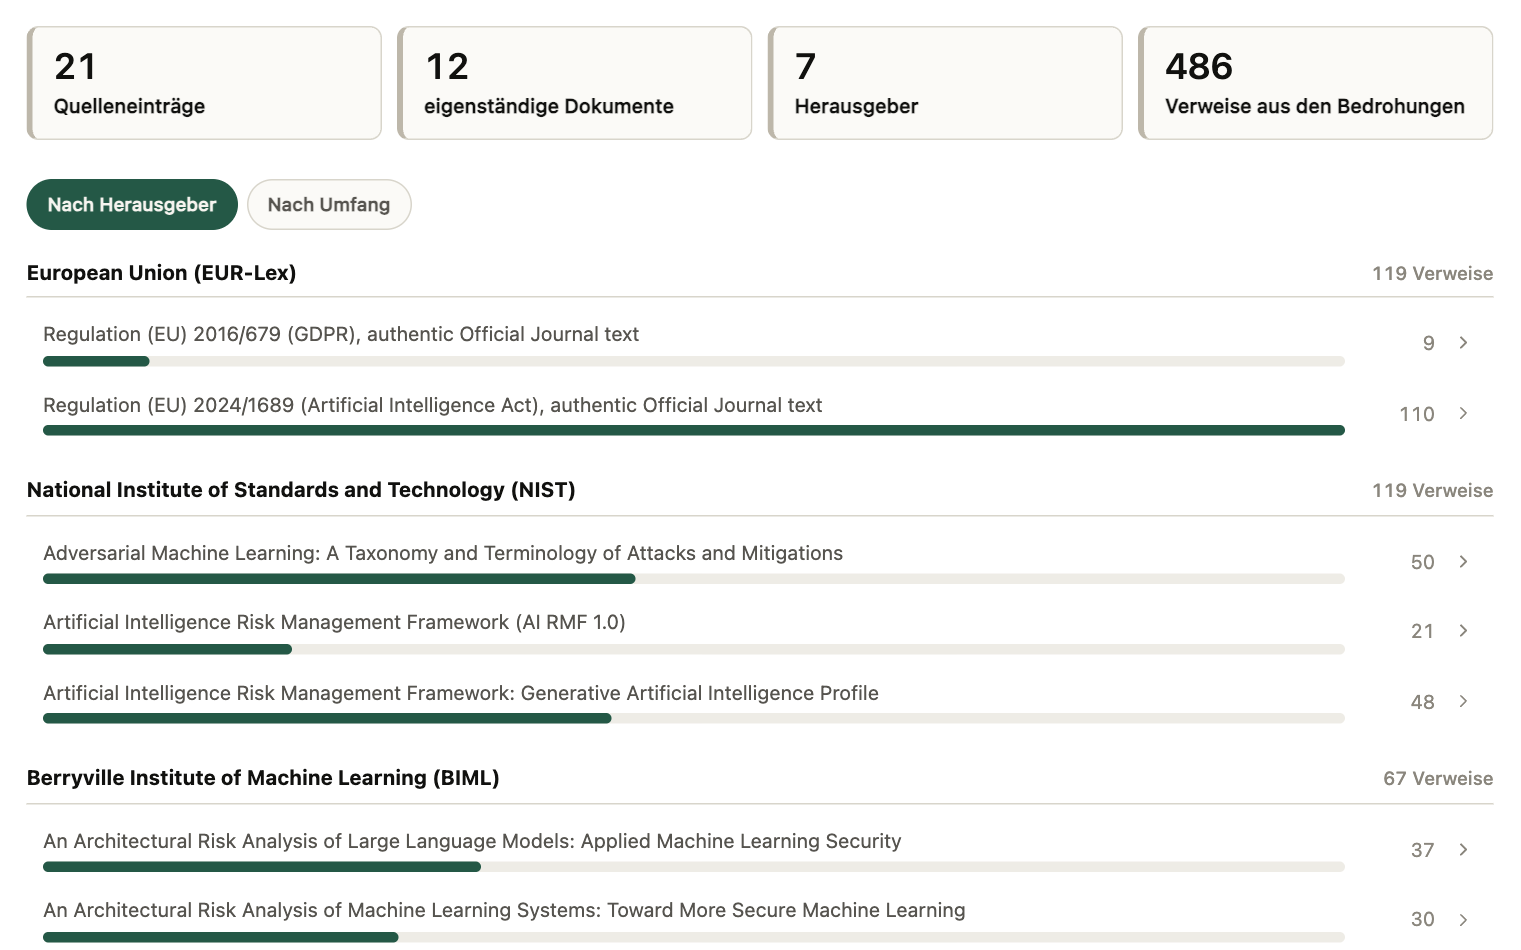
  2. Preview of the analysis: Evidence base Evidence base What is this based on? For assessors, internal audit and anyone judging how solid a source is
Understanding threats
Placing your own system
Planning mitigations

Overview of all ten analyses

Related
Threat catalogue

All 52 threats in full: description, impact, example, mitigations and verified sources.

To the catalogue
EU AI Act quick check

Four short sections along the EU AI Act for a first, non‑binding orientation of your system.

To the quick check
Assess it yourself

The full assessment with system context, threat selection and evidence tracking, free of charge in the browser.

To the live demo