Checking frameworks and evidencePrimary sourcesSVG
The primary sources behind the verified relations
The catalogue backs every relation with a locator in a primary document. The bars show how many references fall to each source entry, grouped by publisher. Selecting an entry shows its version, licence, link and the threats that refer to it.
For assessors, internal audit and anyone judging how solid a source is
Evidence base
12source entries
12distinct documents
7publishers
512references from the threats
European Union (EUR-Lex) 122 references
National Institute of Standards and Technology (NIST) 119 references
OWASP Foundation 74 references
Berryville Institute of Machine Learning (BIML) 67 references
MITRE 66 references
Bundesamt für Sicherheit in der Informationstechnik (BSI) 61 references
European Data Protection Board (EDPB) 3 references
Select a source entry to see its version, licence, locators and the threats that refer to it.
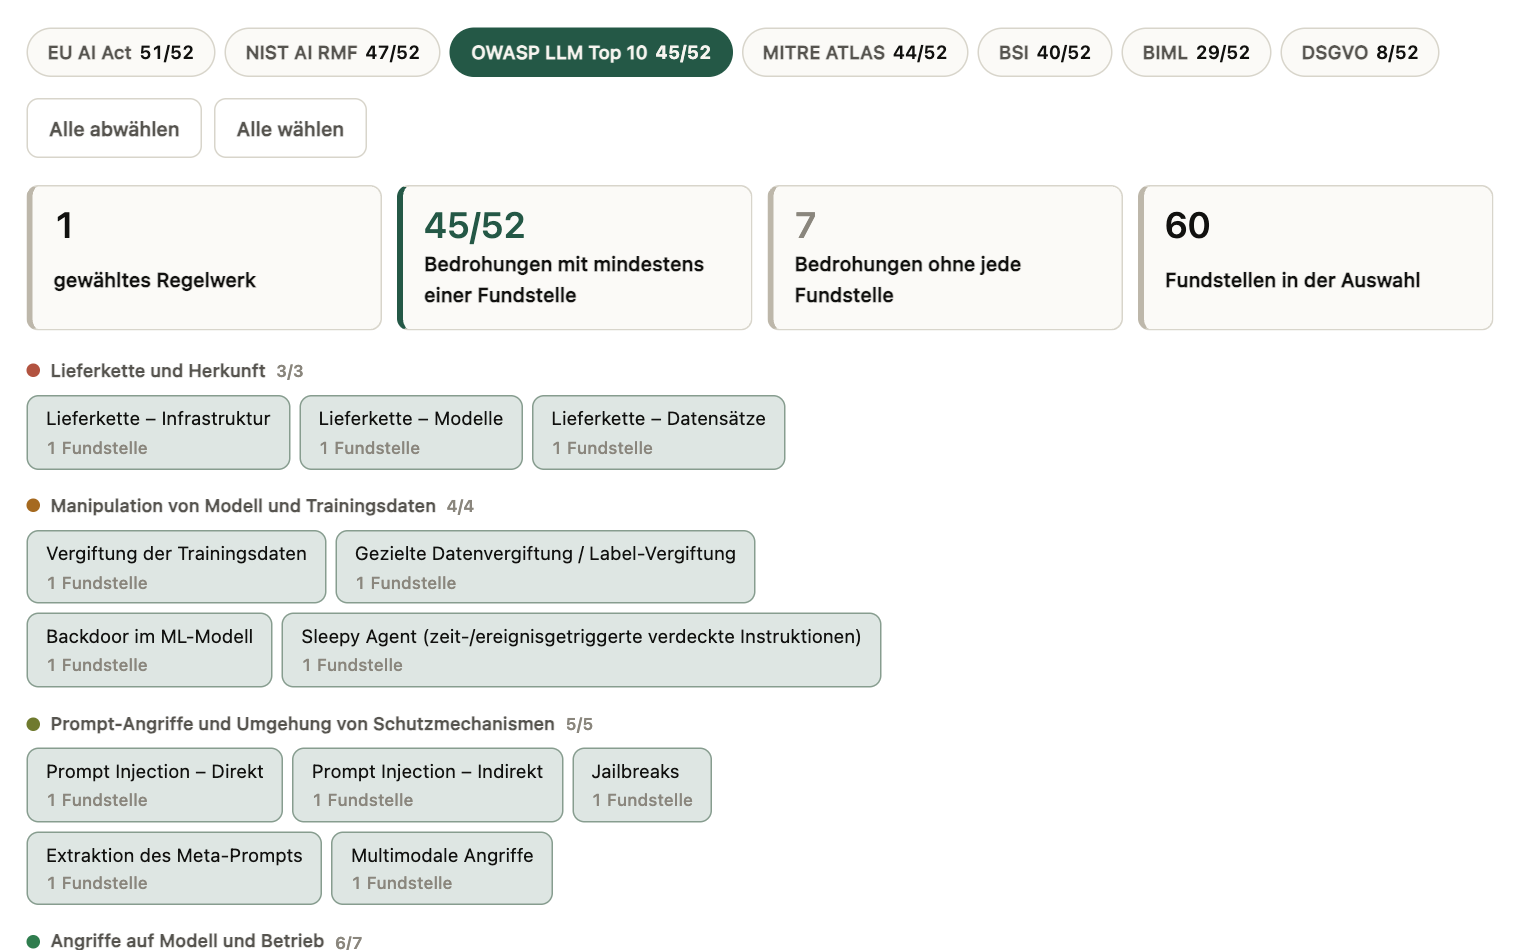
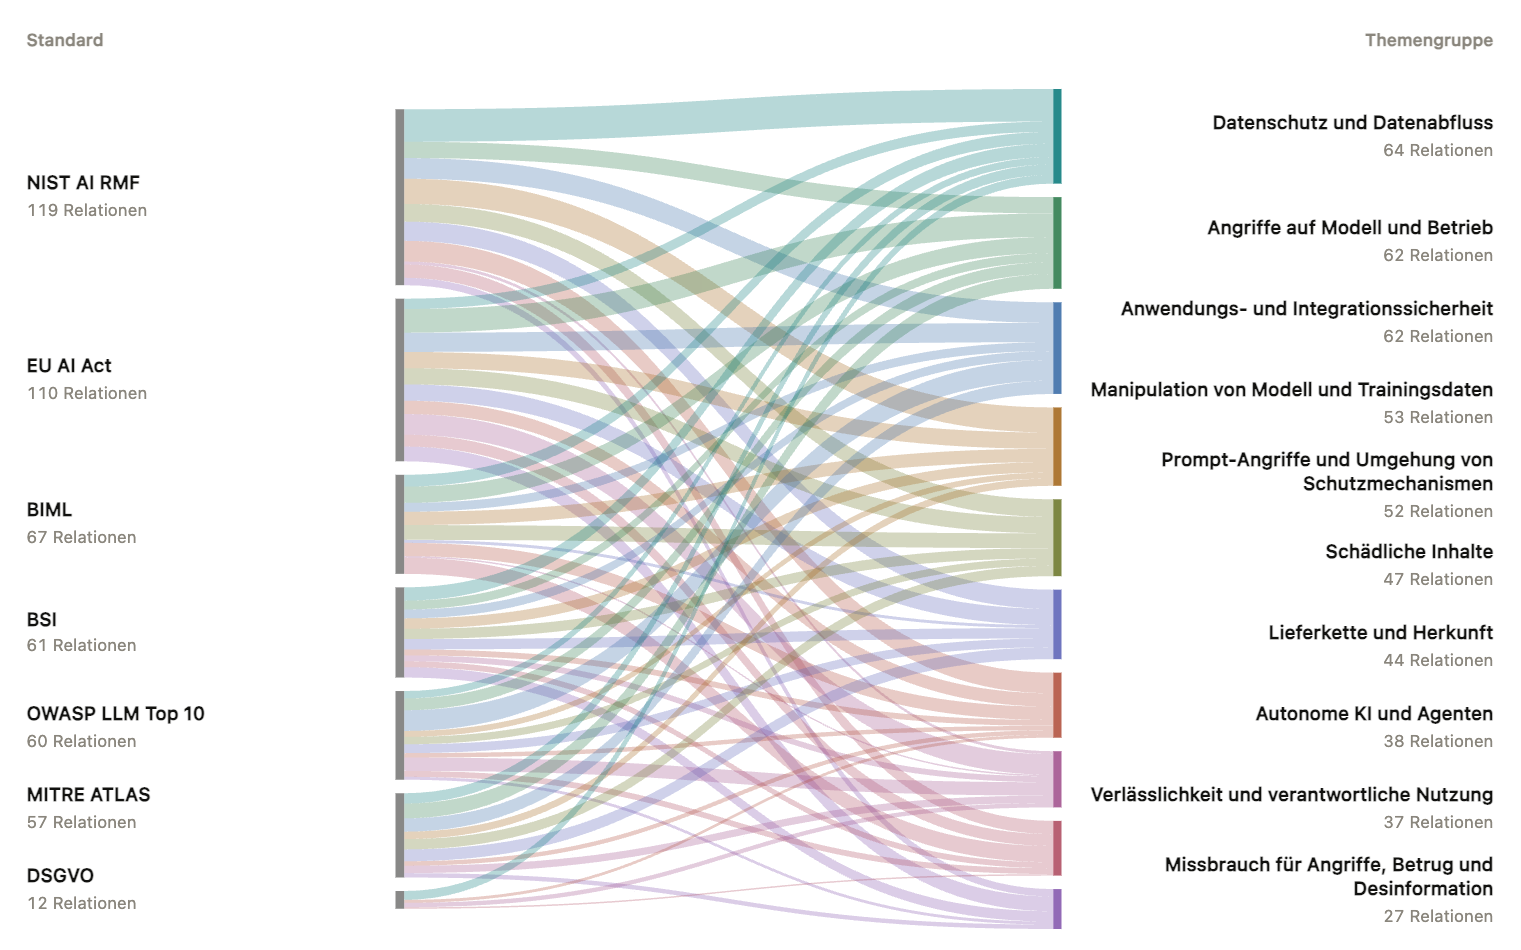
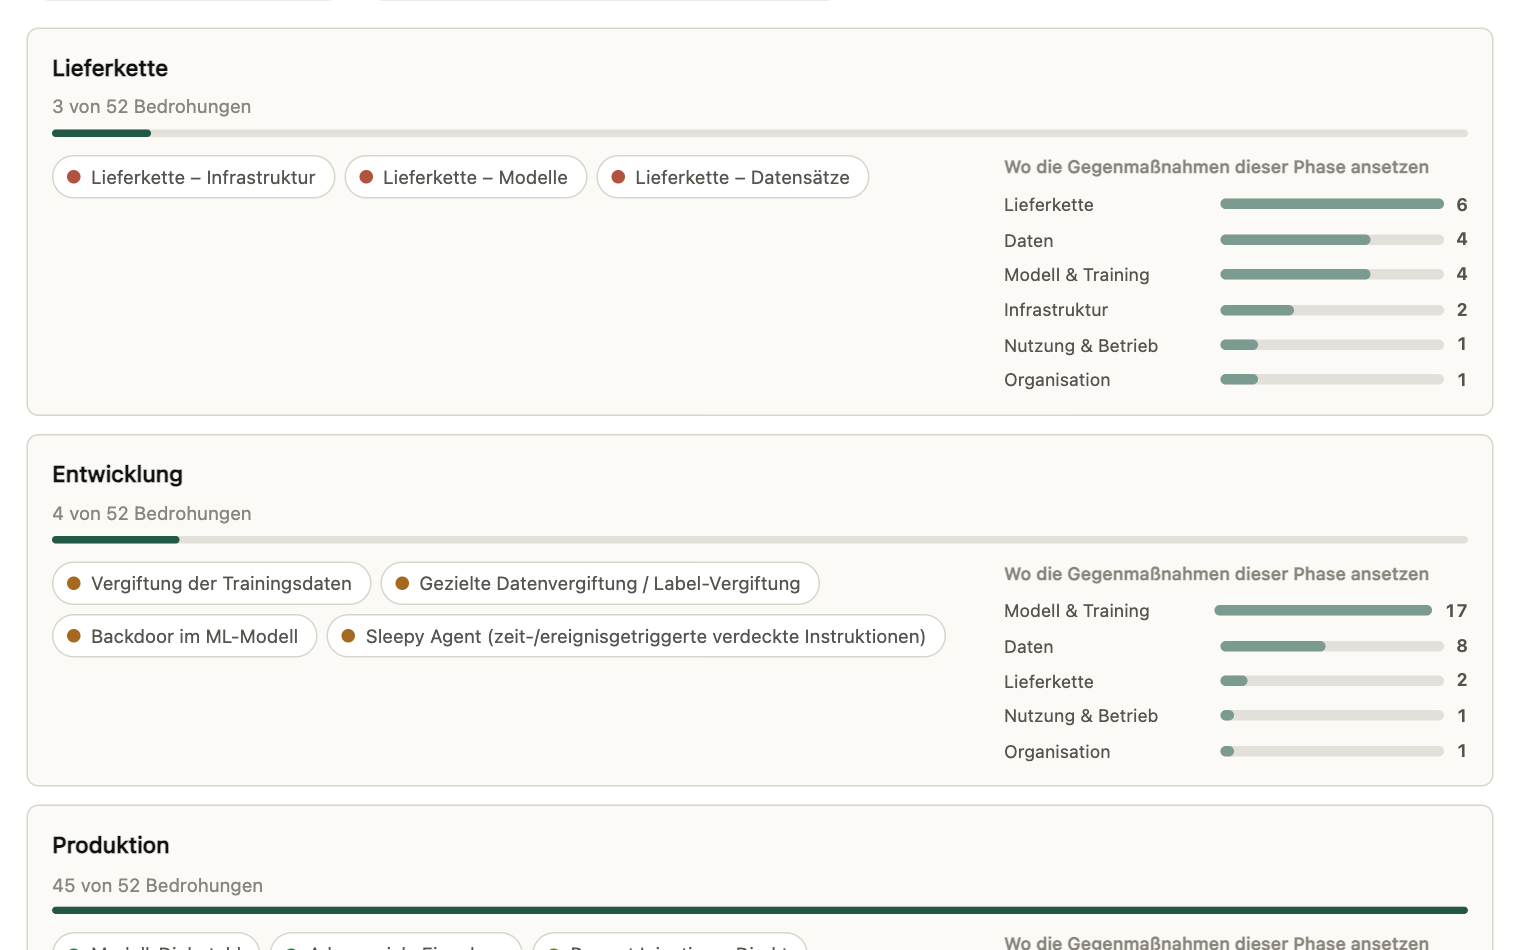
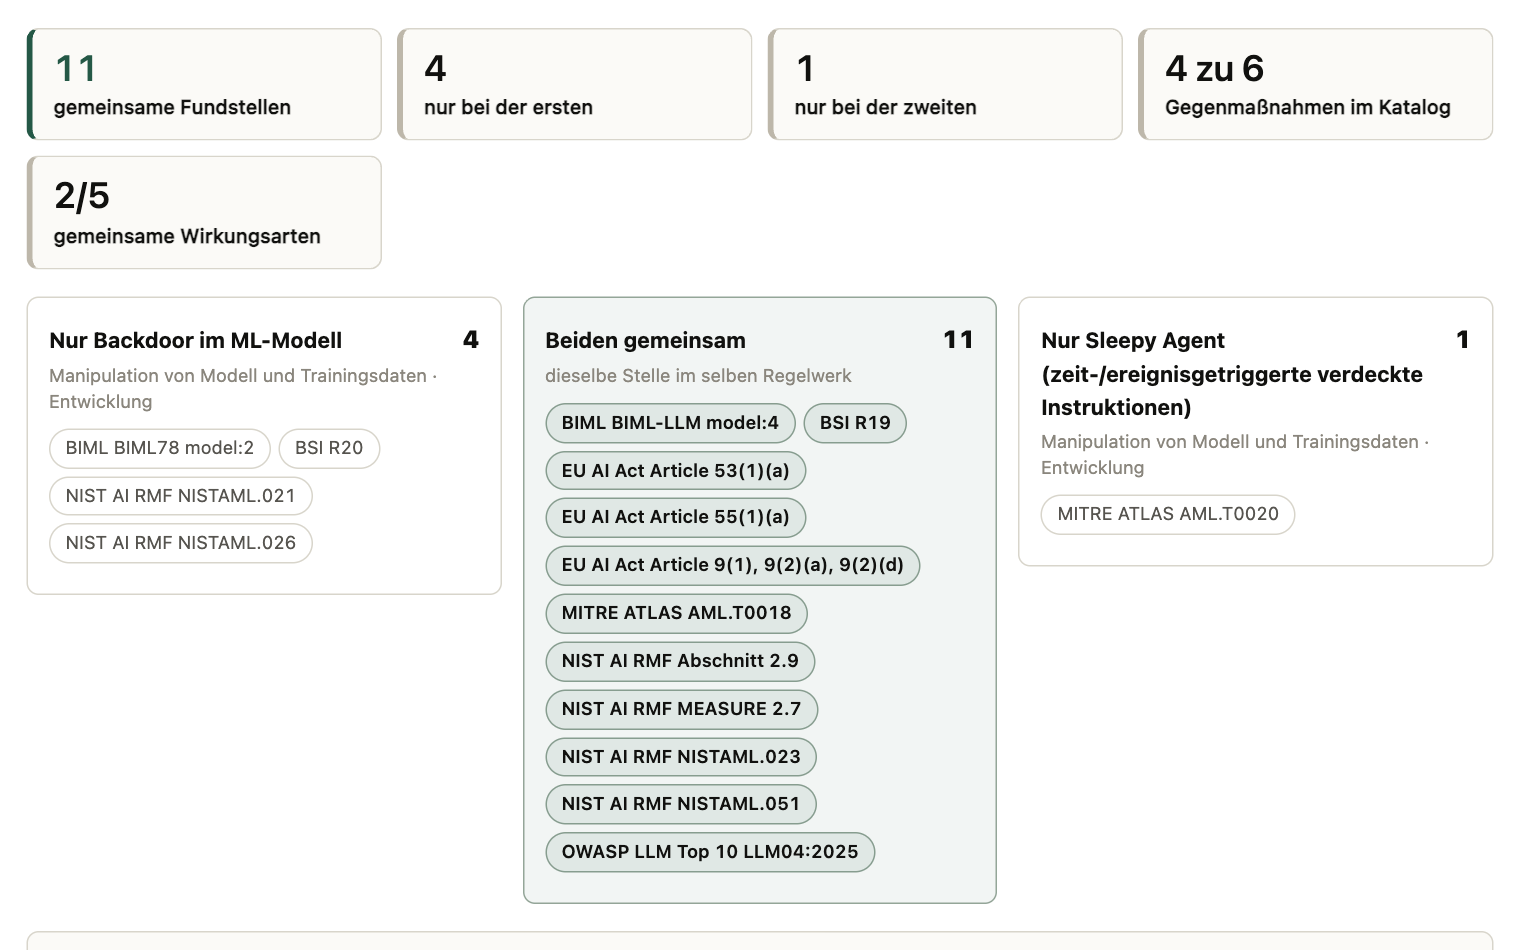
Framework mappingsThe framework mappings show which reference belongs to which topic group.
The file shows the current state including any filters and carries the note, catalogue version and source.
The number counts references from the threats to the source entry, not the size or the weight of the document. Several entries can belong to the same document when they point to different places within it; the locator is then shown before the title.
Versatile AI Risk Assessment is an aid for structuring AI risks and making them transparent. It does not replace legal or professional advice and makes no binding decisions.
Further analyses
The same data, a different question
The other nine analyses, searchable and filterable by perspective like the overview; those of the same perspective first.
Show filters
No filter set, the list shows the complete collection.9 of 9 further analyses
Checking frameworks and evidence
Framework mappings
Where is this anchored professionally and legally?
No result for this selection.
Remove a filter or clear the search. The numbers in the filter column show how many entries the collection holds for each value.
Related
From the analysis to the assessment
All 52 threats in full: description, impact, example, mitigations and verified sources.
To the catalogueSix questions along the EU AI Act and a deadline plan with the obligations that apply to your system.
To the quick checkChoose a role and a risk class and see which EU AI Act obligations apply from when, with legal reference and evidence.
To the obligations compassThe full assessment with system context, threat selection and evidence tracking, free of charge in the browser.
To the live demo