Versatile AI Risk Assessment

Understanding threatsThreats MitigationsSVG

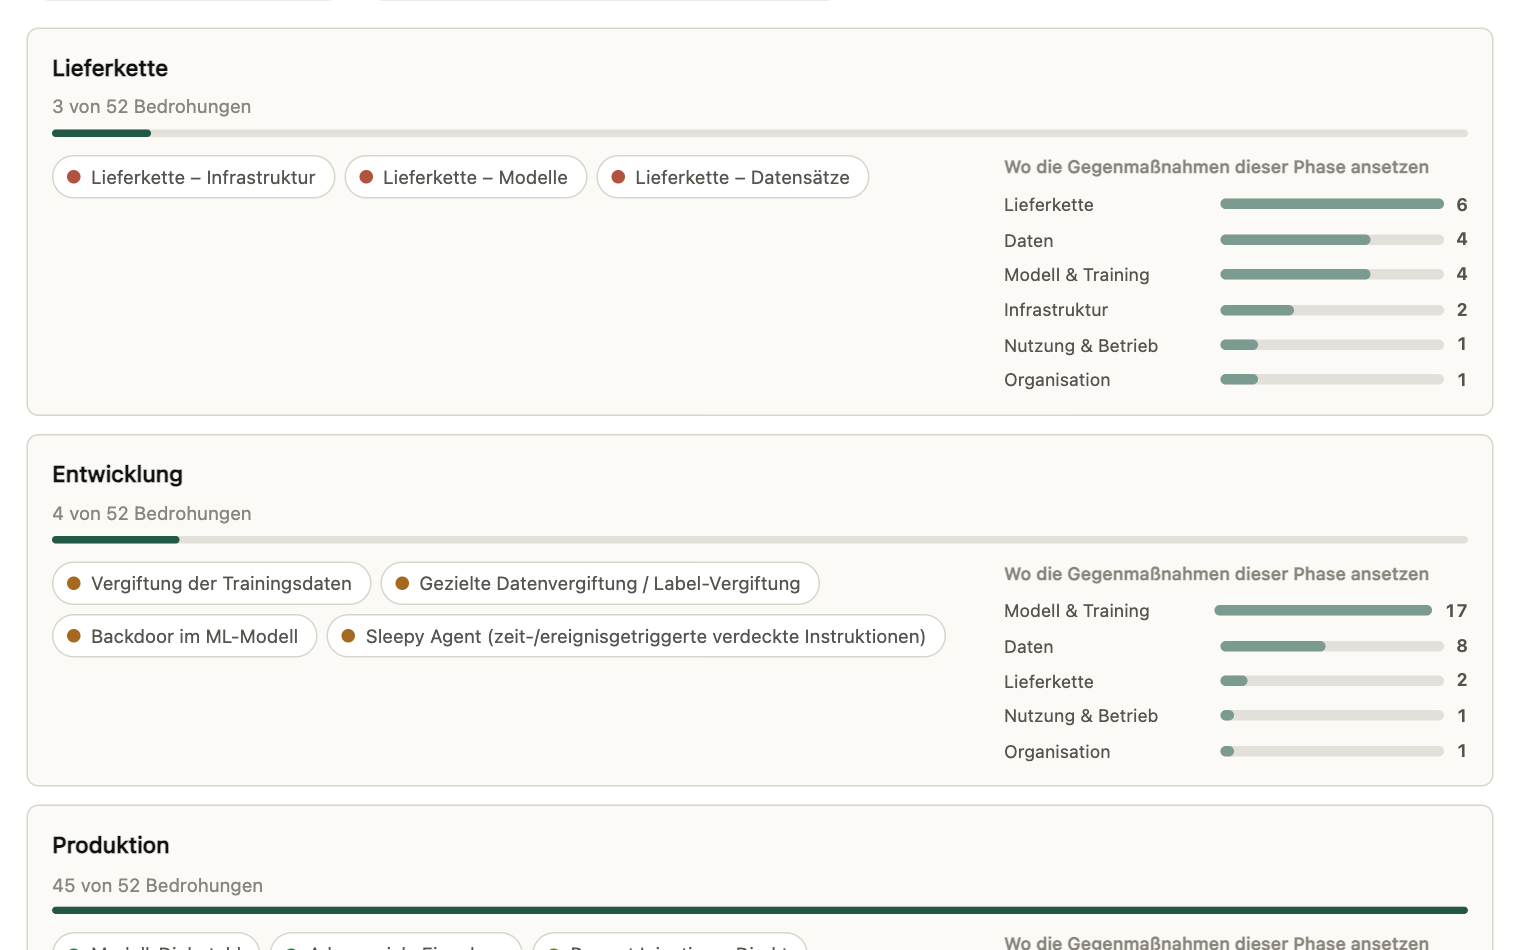
The pathway of a threat and the points where mitigations take effect

Choose one of the 52 threats. The upper track walks through the pathway, the lower one shows the five effect classes the catalogue uses for mitigations. Where the catalogue lists no mitigation for an effect class, a visible gap remains at that point.

For anyone working through a threat in depth for the first time

Threat pathway

All 52 threats to choose from.

Supply Chain – Infrastructure

Supply Chain and Provenance Supply Chain 4 mitigations Full text and sources

The pathway

What it is

Attackers compromise the technical environment in which an AI system is developed and operated: cloud services, development tools, and third-party software components. This gives them access to systems, data, and models.

Where mitigations take effect

0 of 2 available effect classes are covered by at least one mitigation you marked. For 3 effect classes the catalogue lists no mitigation here: Impact-limiting, Corrective, Restorative.

All mitigations for this threat

Tick what is already in place in your organisation. The selection stays in this view and is not stored.

  • Use trusted suppliers

    Effect: Preventive Implementation level: Supply chain Control type: Contracts & third-party management Complementary type: Organizational & process-based

    Reason for the classification

    Primarily a contracts and third-party management control: Selection, verifiable commitments, and audit or enforcement rights toward third parties enable the protective effect; complemented by binding workflows.

  • Infrastructure hardening

    Effect: Preventive Implementation level: Infrastructure Control type: Technical

    Reason for the classification

    Primarily technical: Safe formats, restrictive defaults, or protective layers reduce unsafe execution paths and exploitable attack surface.

  • Supply chain security audits

    Effect: Preventive, Detective Implementation level: Supply chain Control type: Contracts & third-party management Complementary type: Organizational & process-based

    Reason for the classification

    Primarily a contracts and third-party management control: Contractual audit, information, and remediation rights enable control; binding audit workflows put those rights into practice.

  • Continuous monitoring of hosting environments

    Effect: Detective Implementation level: Infrastructure, Use & operations Control type: Technical Complementary type: Organizational & process-based

    Reason for the classification

    Primarily technical: Software or analytical tools systematically produce and evaluate measurements, deviations, or attack indicators; complemented by binding workflows.
The file shows the current state including any filters and carries the note, catalogue version and source.

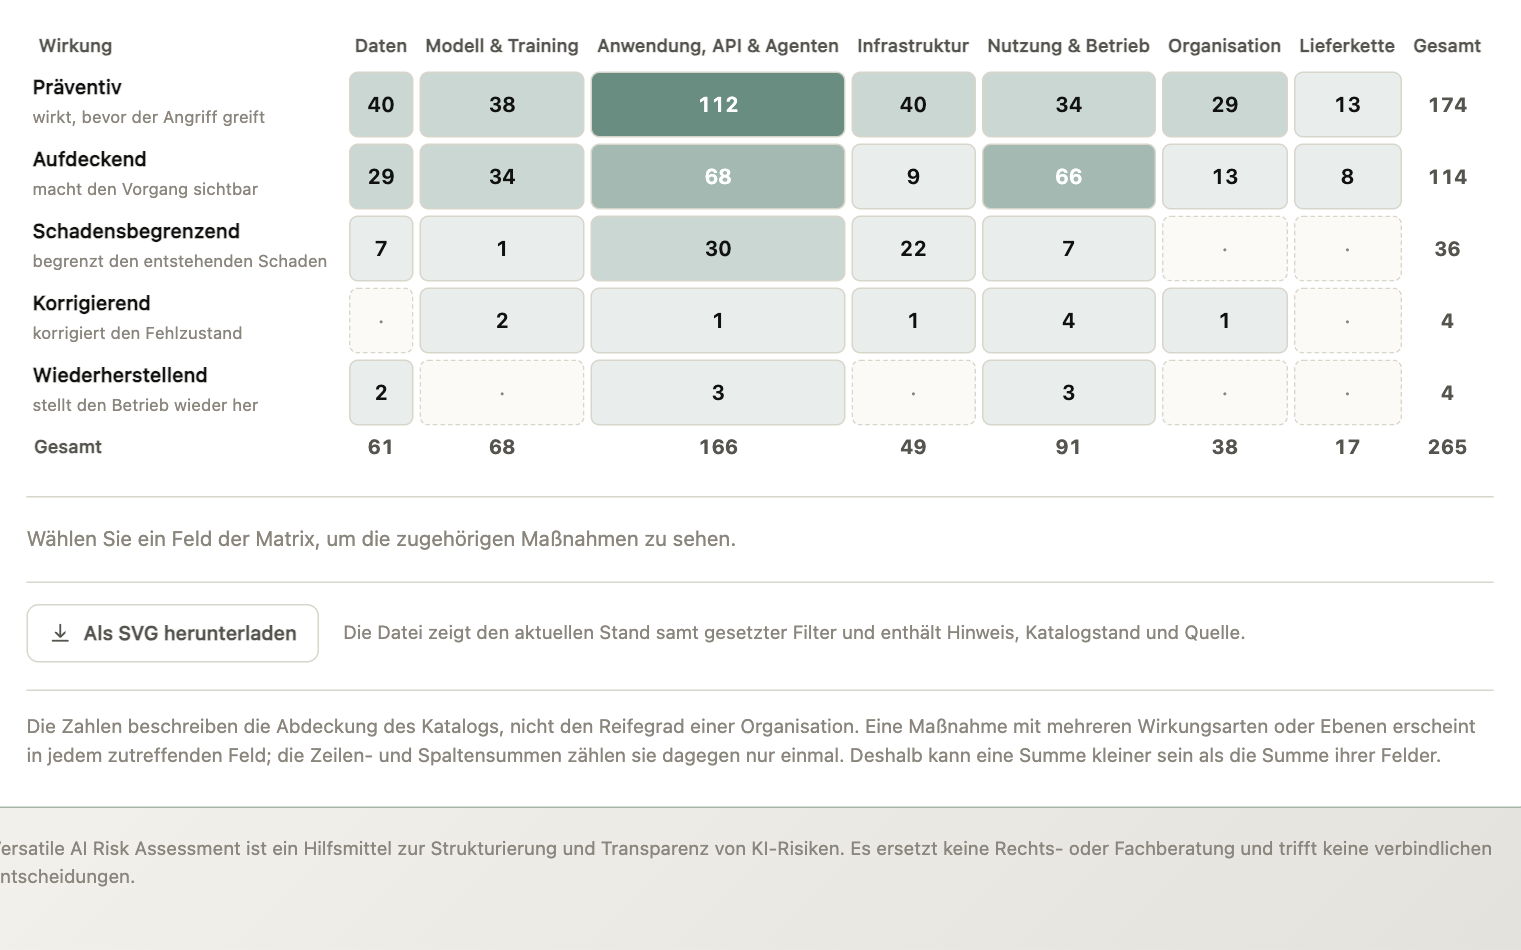
The effect class describes where a mitigation takes effect, not how effective it is in a specific case. A gap means the catalogue lists no mitigation of that effect class for this threat.

Versatile AI Risk Assessment is an aid for structuring AI risks and making them transparent. It does not replace legal or professional advice and makes no binding decisions.

Further analyses

The same data, a different question

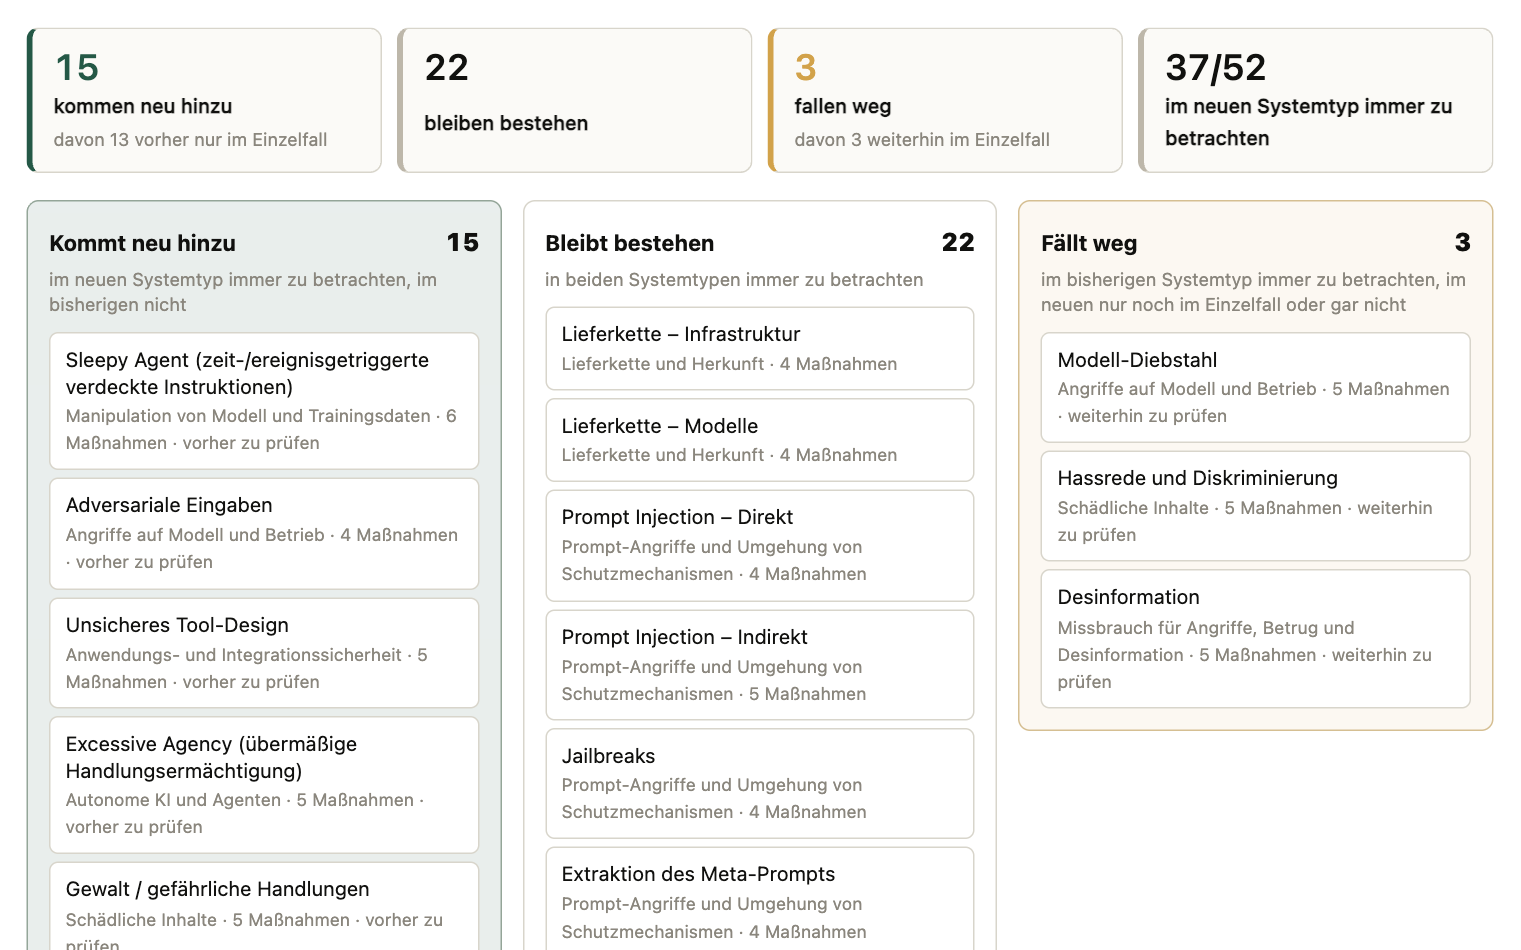
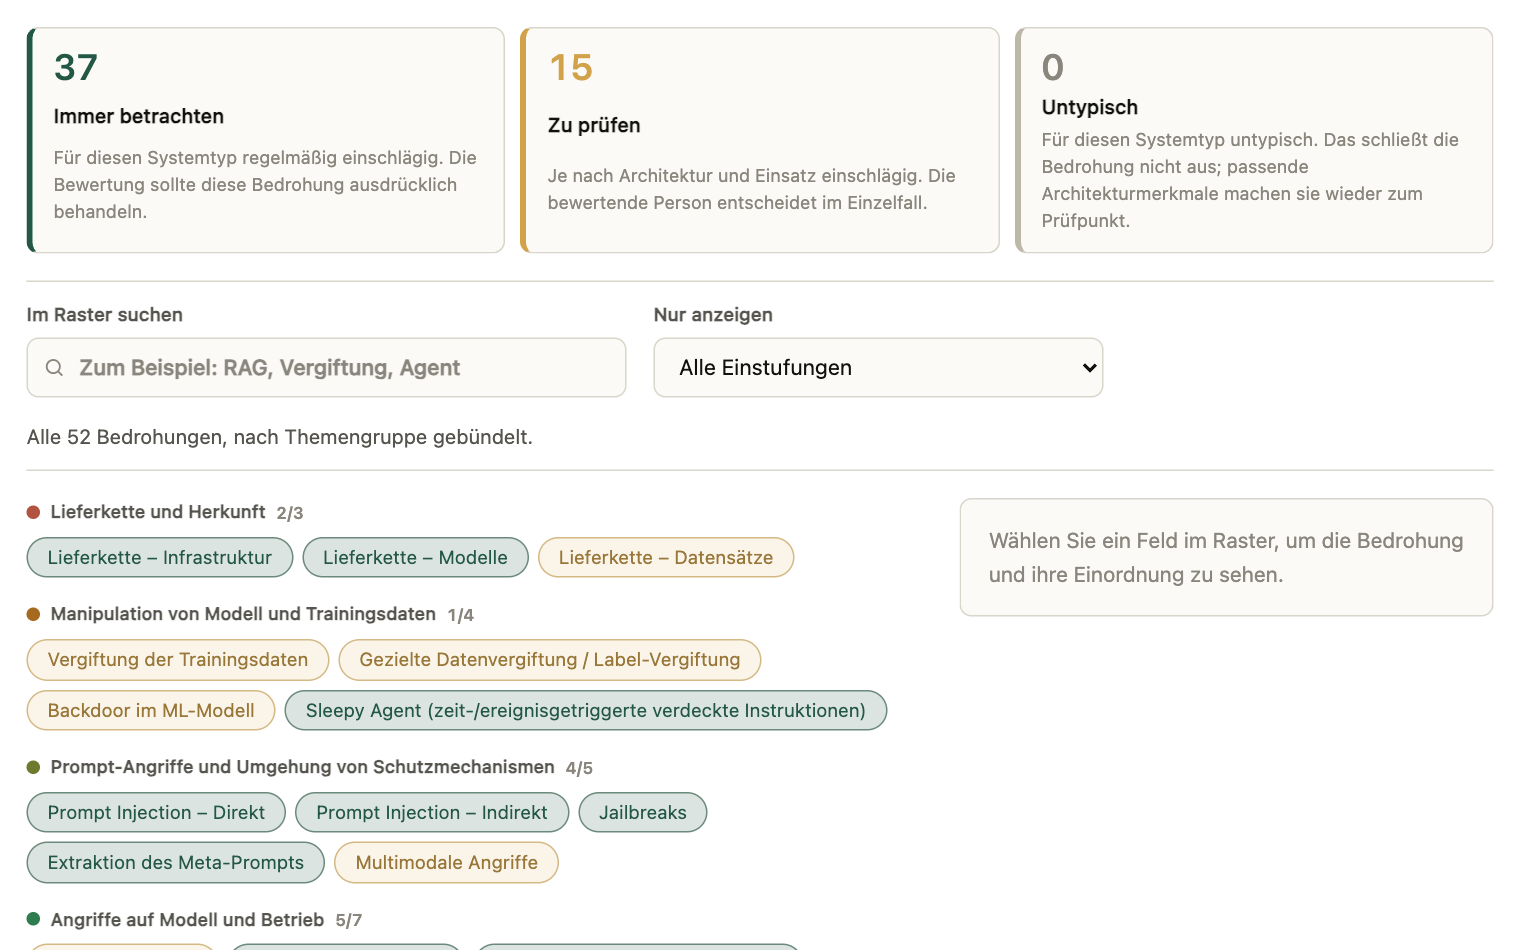
The other nine analyses, searchable and filterable by perspective like the overview; those of the same perspective first.

Show filters
No filter set, the list shows the complete collection.9 of 9 further analyses

Understanding threats

Lifecycle

When does which risk arise?

Placing your own system

System context

Which threats affect my system?

Planning mitigations

Effect matrix

How and where do mitigations take effect?

Planning mitigations

Ownership

What types of mitigations are there?

Checking frameworks and evidence

Coverage gaps

What does my framework not reach?

Checking frameworks and evidence

Evidence base

What is this based on?

Checking frameworks and evidence

Framework mappings

Where is this anchored professionally and legally?

Overview of all ten analyses with all filters

Related
Threat catalogue

All 52 threats in full: description, impact, example, mitigations and verified sources.

To the catalogue
EU AI Act quick check

Six questions along the EU AI Act and a deadline plan with the obligations that apply to your system.

To the quick check
Obligations compass

Choose a role and a risk class and see which EU AI Act obligations apply from when, with legal reference and evidence.

To the obligations compass
Assess it yourself

The full assessment with system context, threat selection and evidence tracking, free of charge in the browser.

To the live demo